WEB PLATFORM / IN DEVELOPMENT
Secure Portfolio Platform
A Flask portfolio and content-management application with database fallbacks, contact protections, response headers, and public-page contract tests.
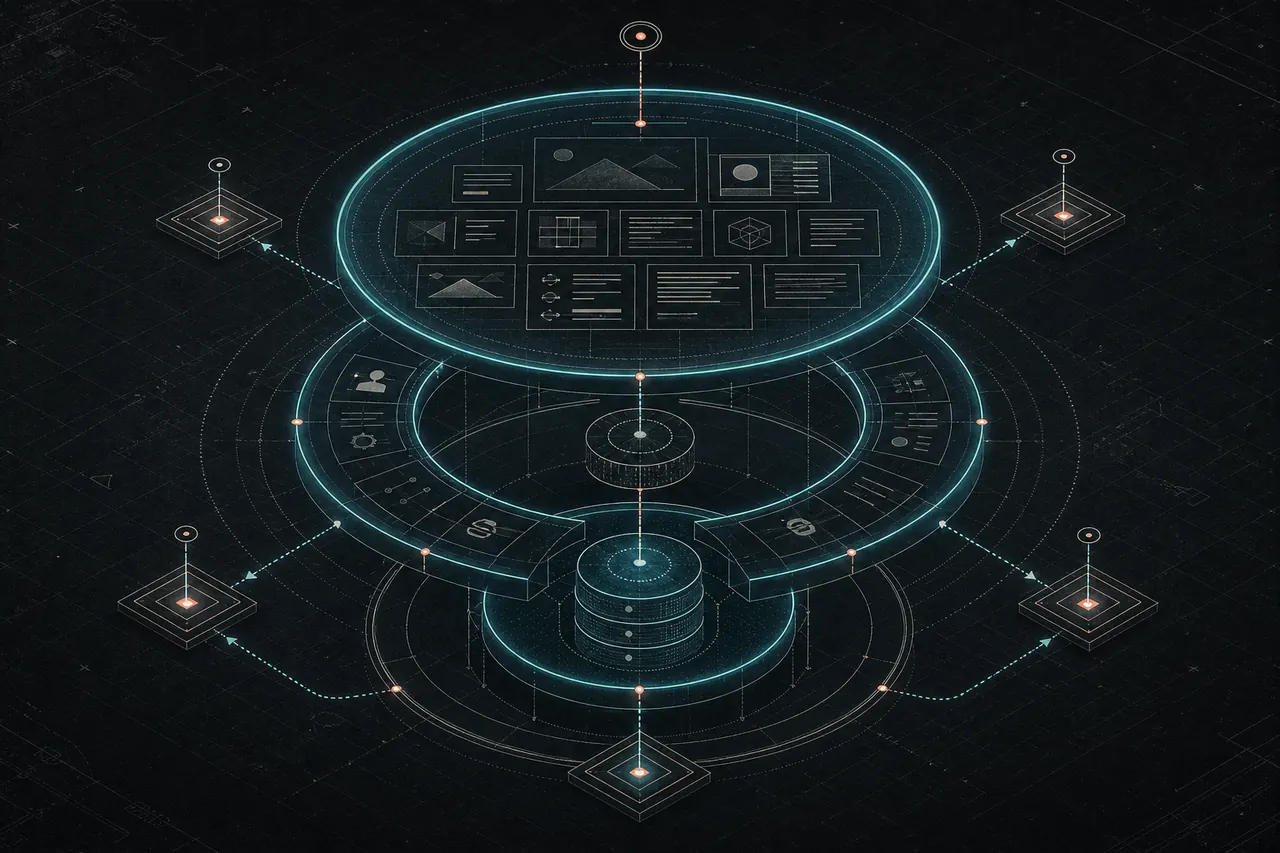
SYSTEM QUESTION
Treat portfolio content, contact submission, administration, and deployment adapters as distinct boundaries with explicit controls and tests.
A public site combines untrusted form input, authenticated administration, mutable content, database variability, and multiple runtime entry points.
DIRECT ANSWER
What does Secure Portfolio Platform do?
A Flask portfolio and content-management application with database fallbacks, contact protections, response headers, and public-page contract tests. It addresses a public site combines untrusted form input, authenticated administration, mutable content, database variability, and multiple runtime entry points.
ROLE & SCOPE
The inspected repository establishes implementation and test artifacts but does not establish an individual contributor role.
The audited slice covers Flask routes, contact CSRF and throttling, response headers, project persistence, database-manager selection, runtime entry points, and public-page tests.
CONSTRAINTS
The contact limiter is process-local, and deployment configuration does not by itself prove a live production deployment.
ARCHITECTURE
-
Flask routes and templates
serve public, blog, contact, project, and administrative views
app.py -
Unified models
select database-manager implementations and normalize project records
models/project_model.py -
MySQL or Supabase
persist managed content through selected database adapters
database_manager.py -
Runtime entry points
run the Flask application as a Gunicorn web service on Render
render.yaml
TRUST BOUNDARIES
Browser to contact handler
Names, addresses, subjects, and message text enter validation, persistence, and mail paths.
app.pyApplication to database provider
Content records cross either a MySQL connection or Supabase client and REST paths.
database_manager.py
SECURITY DECISIONS
Cross-site or automated contact submissions.
The contact POST validates a session token, applies a per-client process-local limit, and bounds input lengths.
app.pyBrowser interpretation and framing of public responses.
An after-request hook sets content-type, frame, referrer, content-security, and conditional transport headers.
app.pyIMPLEMENTATION EVIDENCE
app.pyPublic and security controls
The Flask application implements route handling, CSRF checks, throttling, validation, and response headers.
models/project_model.pyContent persistence
Project records retain integer route compatibility and select provider-specific database managers.
tests/test_public_pages.pyPublic-page contracts
The pytest suite exercises public pages, contact markup, project details, blog views, and shared not-found rendering.
render.yamlRender deployment definition
The Render Blueprint runs the Flask app with Gunicorn, selects Supabase, and configures the health check.
VERIFIED OUTCOMES
The public route and sparse project-detail contracts are executable in pytest.
tests/test_public_pages.pyThe project model supports MySQL and Supabase-oriented persistence paths without changing its public methods.
models/project_model.py
OPEN HARDENING
Move contact throttling to shared storage before relying on it across multiple processes.
app.py